AI is changing security testing. Are organisations ready?
The time between a weakness being identified and exploited is narrowing. For security leaders, the challenge is no longer simply finding vulnerabilities faster. It’s understanding which weaknesses pose the greatest risk and how to keep pace as their environments evolve.
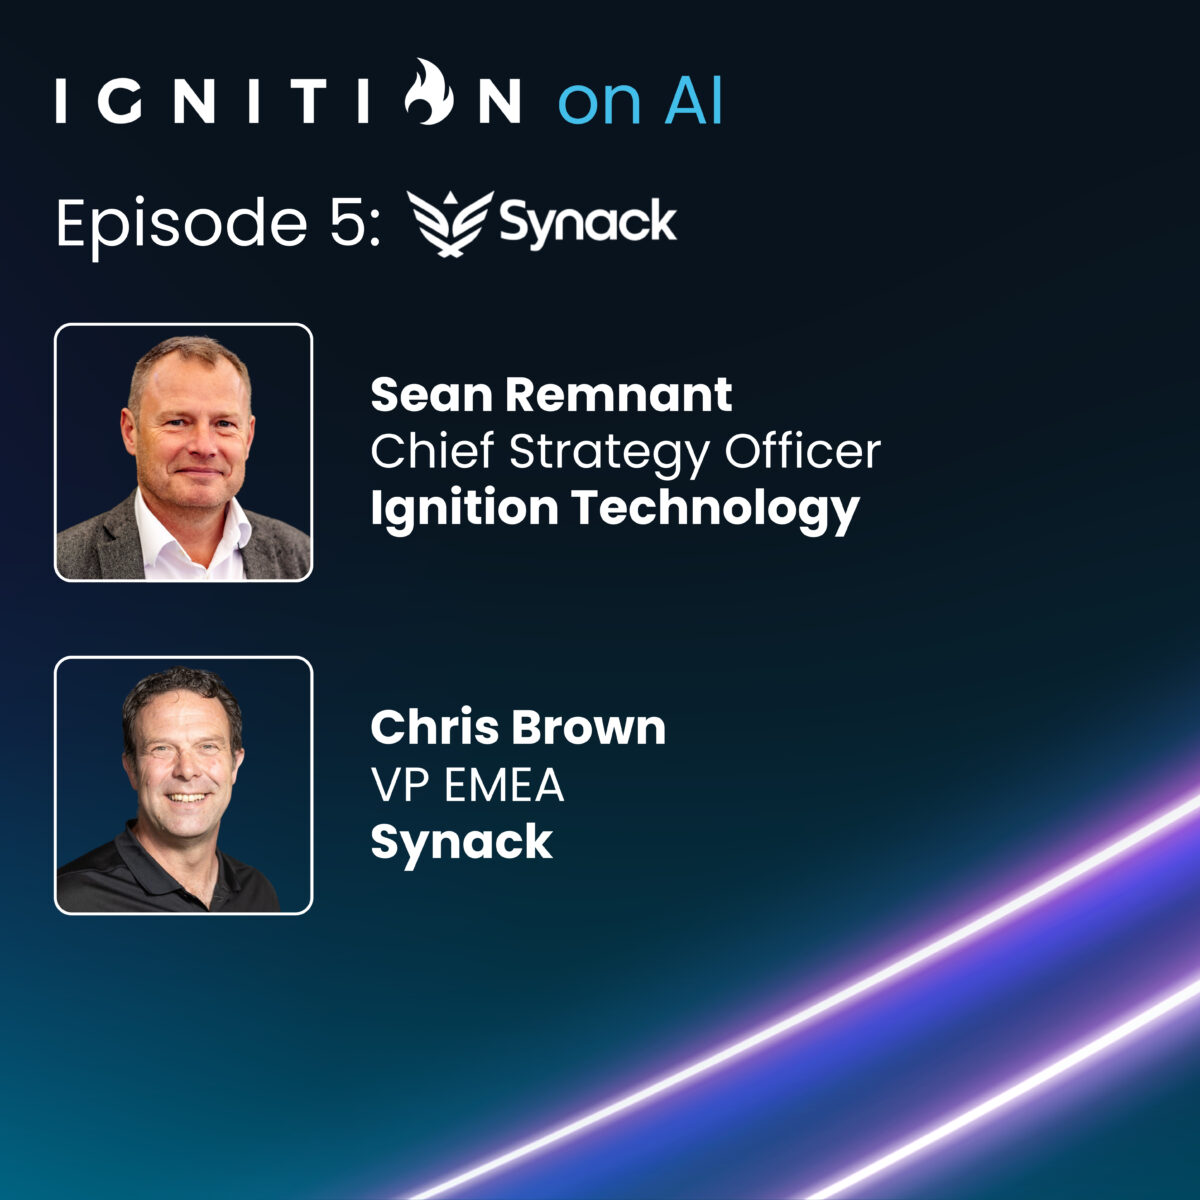
On our fifth episode of the Ignition on AI video podcast series, Ignition Technology’s Chief Strategy Officer, Sean Remnant is joined by Chris Brown, VP EMEA at Synack to discuss how security leaders can adapt their strategies to keep up with new AI technologies.
How AI is changing offensive security
With new AI technologies constantly emerging, AI is increasing the speed and scale of vulnerability discovery, while making exploitation faster. This is generating interest in AI-powered testing at board level amongst security practitioners.
This asks the question: how can organisations use AI to strengthen their security posture without mistaking faster testing for better protection?
AI-powered testing: more findings but what do they mean?
AI-powered testing is detecting vulnerabilities within systems faster than ever before as they cover large attack surfaces efficiently.
While AI is useful, humans can still uncover more critical vulnerabilities by applying context to understand how systems work and interact. A blended approach of human knowledge and AI can help organisations move from raw findings to meaningful risk prioritisation.
Testing the AI organisations are using
To manage threats, organisations must consider the security of the AI applications and infrastructure they introduce.
In the episode, Chris mentions that many Synack customers ask for AI chatbots and backend systems to be tested to identify vulnerabilities and potential process risks, when recognising that testing whether an AI-system behaves as intended can be more complex.
Build, buy or blend? The challenges of AI security testing
There’s increasing pressure on organisations to invest in AI and develop their own testing capabilities to deal with threats.
Chris raises important questions about the long-term costs of maintaining in-house tools, the resources needed to keep testing frameworks up to date, and the pace of technological change.
Security leaders need a clear strategy, a realistic understanding of the commitment involved and a model that suits their organisational capabilities.
Start with risk, not the technology
For security leaders developing an AI testing strategy, the starting point should be a clear understanding of what they’re trying to achieve.
Organisations must distinguish between testing to satisfy compliance and testing to genuinely strengthen their risk posture.
An effective strategy isn’t about adopting AI for its own sake and to keep up with trends. It’s about choosing the right combination of technologies, expertise and testing frequency to improve security as the business evolves.
Watch the full episode of Ignition on AI to see how AI is reshaping offensive security.
Subscribe to the Ignition Technology YouTube channel to catch future episodes of Ignition on AI.